A GitHub app for pull requests

Catch security and PII risks before you merge.

AI now writes much of your code, and it can open doors an attacker will find. CodeMD is a GitHub app that checks every pull request and maps the risk paths in your code: the routes outside input can take to your secrets and your customers' personal data. Knowing those paths helps you prepare for cyber attacks, external attacks and security vulnerabilities, and you only run the tests that matter for the change.

Install on GitHub See an example PR check

  1. 1 Install the GitHub app
  2. 2 Open a pull request
  3. 3 Three checks appear on the PR

Example results on a pull request

What the checks show before you grant access.

CodeMD Call-Path Security✗ Would have failed

A real case, replayed on the commit that added the bug.

Path the check reports
MCP tool call from an AI agent → runNmapScan: process/shell execution
Commit it fails on
“Add files via upload”, January 9, 2025
Advisory
GHSA-xc68-rrqc-qgq3 · CVE-2026-3484 · published about 14 months later

See all 14 real cases →

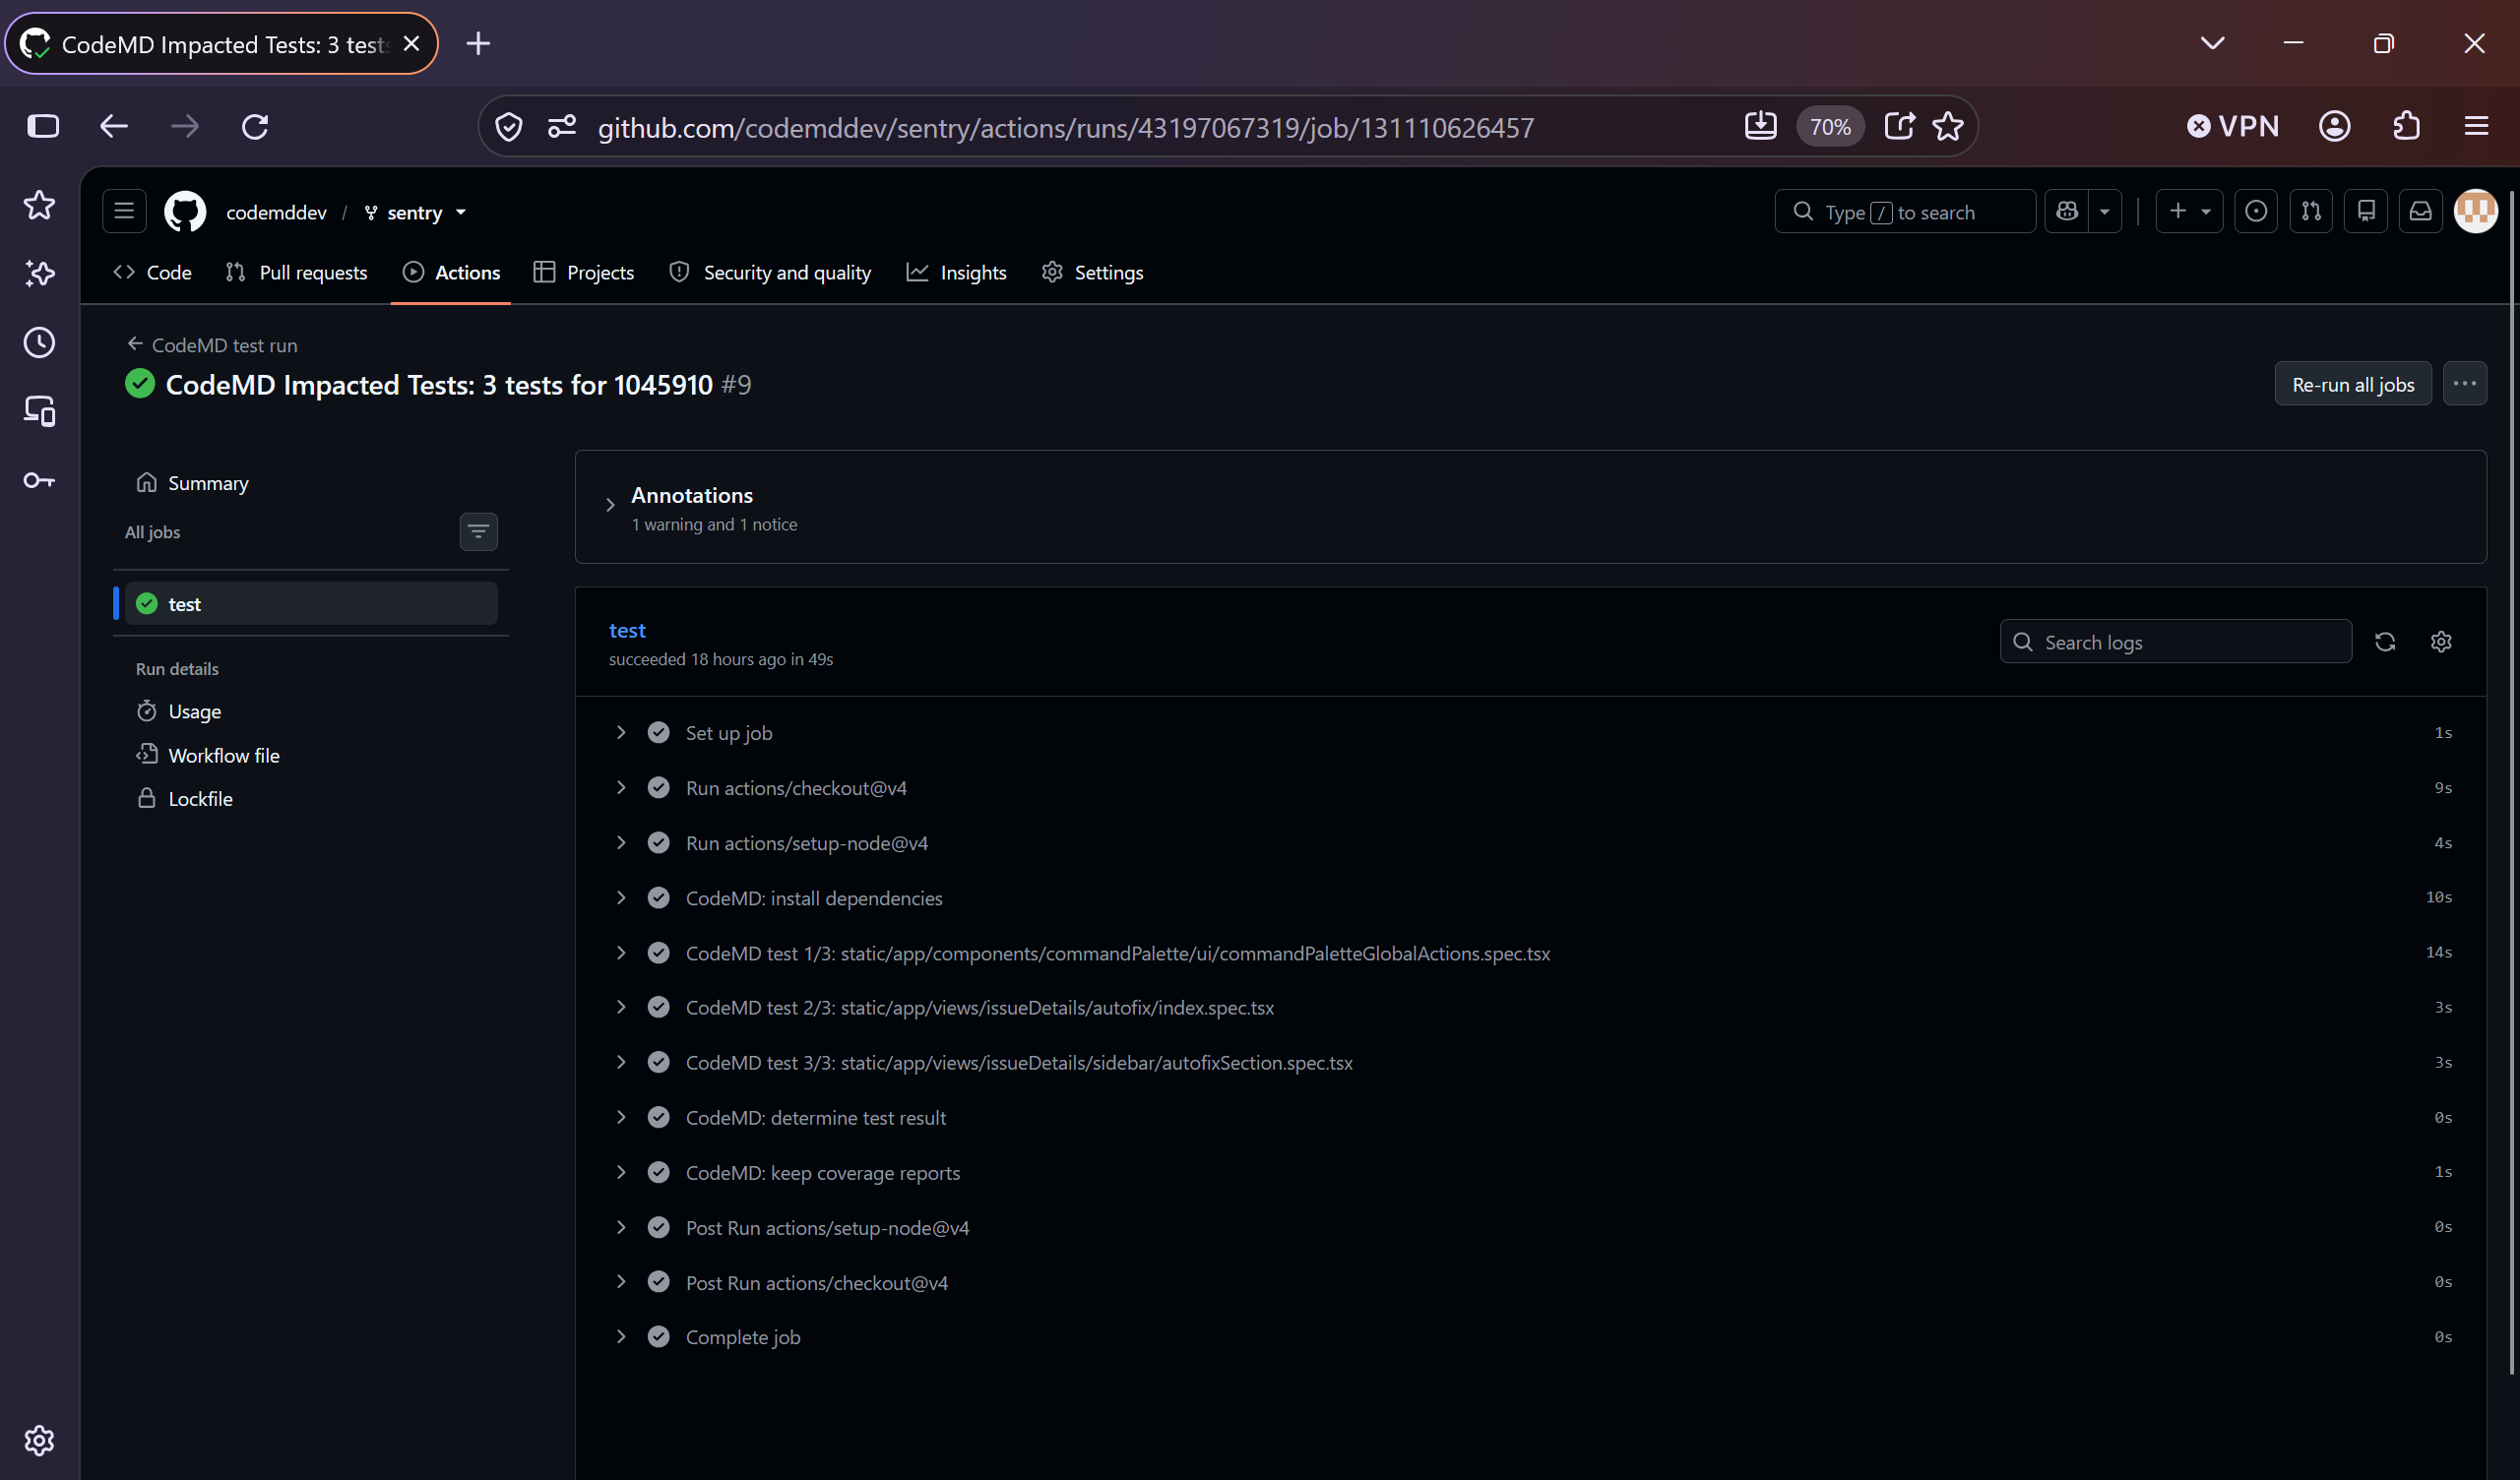
CodeMD Commit Impacted Test Runs✓ Tests passed

Example output on a pull request.

GitHub CodeMD Commit Impacted Test Runs result showing three impacted tests passed

What the app does

Three checks on every pull request, right where your team already reviews code.

Check 1 · Free

Call-Path Security

AI assistants write code quickly, and a change can open a door an attacker may later find. On each pull request, CodeMD checks whether anything an outsider can send (a web request, a form field, a message) can newly reach code that could do damage. If it can, the check fails and shows the path, so you can fix it while it costs a code review, not a breach. What it looks for, and how that helps:

  • Commands run on your server. Helps lower the chance of an attacker running their own commands, a common route to stolen data or a taken-over server.
  • Database queries built from text (SQL injection). Helps lower the chance of someone reading or changing your customer records through a form field or a web address.
  • Outside text run as code (eval, unsafe deserialization). Helps keep an attacker's input from being executed inside your application.
  • HTML written into a page (cross-site scripting). Helps keep one visitor's script from running in another visitor's browser, where it can steal a sign-in session.
  • Files served from a path in a variable (path traversal). Helps lower the chance of config files, keys or other private files being read by someone who shouldn't.
  • Redirects to an address in a variable. Helps keep your own links from being used to send customers to a phishing site.
  • File writes and deletes, git operations, outbound requests. Helps flag outside input that could overwrite files, drive changes to your repository, or make your server contact places it shouldn't.
  • Personal data (PII). Looks for passwords and API keys, government IDs, health, payment and bank details, biometrics, names, contact details and location that a change returns, logs or puts in a URL where outside input can reach it, and notes whether a sign-in check is on the path. Helps you spot a possible leak of customer data before it can become a breach notice, a fine or lost trust.
  • Web endpoints. Lists new or wider endpoints and whether each shows a sign-in check, so you can see which doors are open to the public.
  • Only what this change added. Problems already in your code don't fail the check, so review time goes to what you're about to ship.
Check 2 · Free

Commit-Relevant Test Runs

A change can break something several calls away from the line you edited. CodeMD finds the tests connected to your change and runs them, so problems are more likely to be found before your customers find them.

  • Finds the tests that matter for this change by following call paths. That can mean less time waiting on CI and fewer GitHub Actions minutes spent than running the whole suite.
  • Runs them in your own GitHub Actions and reports pass or fail on the pull request, so a reviewer sees the evidence without running anything.
  • Reports changed-line coverage where it can be measured, so you can see whether the tests that passed actually ran the lines you changed.
  • Files real failures as bugs with the commit, function and test, so they can be fixed while the change is still fresh.
Check 3 · Pro · Informational

Feature Impact

A small edit can reach a lot of your product. This check shows, in plain terms, how far a pull request reaches and which product features it touches, so a reviewer knows how much care it needs. It never fails a pull request.

  • An impact score out of 100 with a level (low to wide), worked out from the call paths the change reaches.
  • The product features it touches, using your own product & features list when you have one.
  • The tests relevant to those features, so you can see what covers the change.
  • Runs only for a paid Pro developer. It uses AI, so it is never run automatically for a free account.
  • Names, not code, go to an AI. To name the features, route paths, button text and function names (never source code) are sent to Anthropic's Claude.

What happens to your code

Your tests run in your GitHub Actions. We keep results, not code.

Details in the privacy policy.

How it works

From the pushed change to the merge decision.

1

Install the GitHub app

Add CodeMD PR Checks to your repository. There is nothing to install on developer machines.

Install GitHub PR Checks →
2

Every pull request is checked

CodeMD looks for new ways outside input could reach risky code or personal data, and runs the tests connected to your change in the repository's GitHub Actions. It runs existing tests for Python, JavaScript/TypeScript, Go, Rust, Java, Kotlin, C#, PHP and Ruby.

3

See the evidence

The PR Checks Dashboard shows what passed, what needs review and where risk remains. Changed-line coverage is reported for Python, JavaScript/TypeScript and Go, with a downloadable Cobertura XML report compatible with GitHub Code Quality and other coverage tools.

Open the PR Checks Dashboard →